
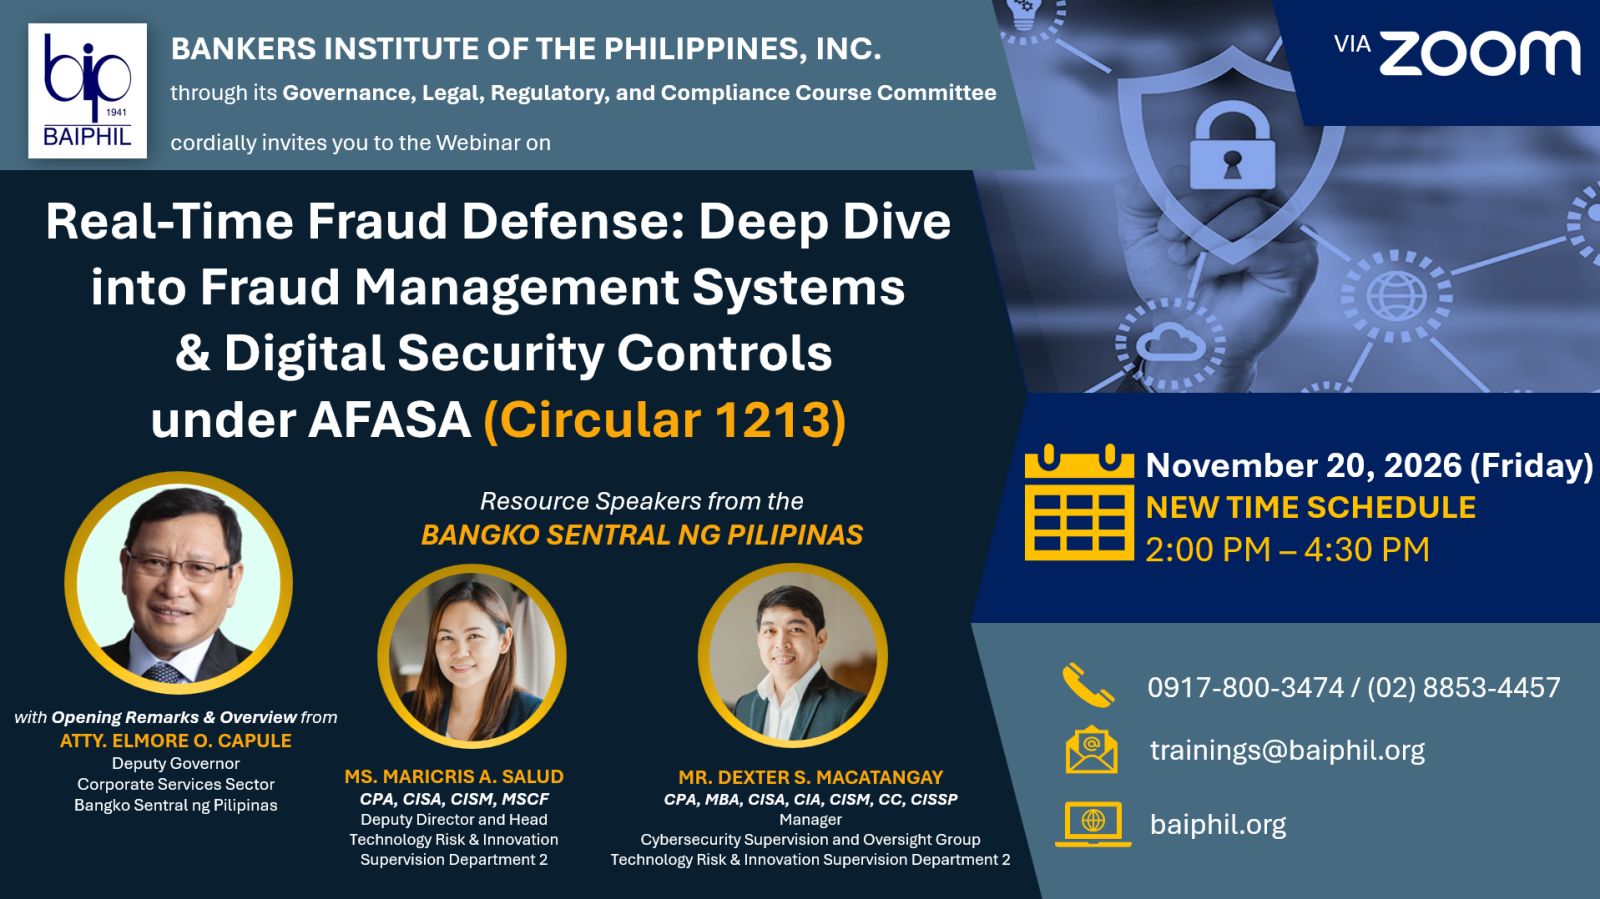
Description
Course Objective:
This course aims to equip participants with a comprehensive understanding of the objectives and control requirements prescribed under BSP Circular No. 1213, Series of 2025, which amended the Information Technology Risk Management regulations to implement Section 6 of the Anti-Financial Account Scamming Act (AFASA). Participants will gain an understanding of the regulatory expectations and practical considerations for implementing these controls to effectively manage fraud risks associated with digital transactions, thereby helping maintain public trust and confidence in the digital financial system.
Brief Description:
Republic Act (R.A.) No. 12010, or the Anti-Financial Account Scamming Act (AFASA), aims to combat financial scams, protect consumers, and uphold the integrity of the financial system. To support the implementation of Section 6 of AFASA, the Bangko Sentral ng Pilipinas (BSP) issued Circular No. 1213, which strengthens information technology risk management requirements and reinforces the responsibility of Bangko Sentral-Supervised Institutions (BSIs) to implement adequate risk management systems and controls to safeguard clients’ financial accounts. The Circular further enhances the existing cybersecurity and technology risk management requirements under the Manual of Regulations for Banks, Non-Bank Financial Institutions, and Payment Systems. This course is designed to deepen participants’ understanding of BSP Circular No. 1213, translate its requirements into actionable strategies, and promote a risk-based culture that proactively addresses emerging fraud risks and trends.
Course Outline
- Overview of AFASA and BSP Circular No. 1213
- Fraud monitoring, detection, and response
- Scope, coverage, and supervisory expectations for FMS
- Minimum and robust fraud management system features
- Policies, procedures, and governance for effective fraud risk management
- FMS requirement for Clearing Switch Operators (CSOs)
- Digital security measures
- Security controls for digital products and services to mitigate risks on cyberattacks, unauthorized access, and fraudulent transactions.
- Strong authentication mechanisms
- Consumer protection tools
- Customer empowerment tools, knowledge, and support to proactively protect their financial accounts
- Other relevant controls
- Layered controls to mitigate the prevalence of financial fraud and scams
- Shared accountability framework
- Roles and responsibilities of BSIs, customers, and other stakeholders
- Liability considerations and allocation of responsibilities
- Collaboration and coordination in preventing and responding to unauthorized transactions
- Implementation considerations and supervisory expectations
- Common implementation approaches and supervisory observations
Target Participants:
Representatives from all interested BAIPHIL member/non-member banks and other financial institutions under BSP jurisdiction, particularly the following:
- Board of Directors
- Senior Management
- Chief Technology Officer
- IT Officers
- Fraud Management Officers
- CCO and Compliance Officers
- CRO and Risk Officers
- CAE and Audit Officers
- Branch Banking Sector
- Regional/Branch Heads, or any authorized branch personnel
- Personnel from Consumer Protection Department/Unit
- Legal Department/Group
Opening Remarks and Overview:
ATTY. ELMORE O. CAPULE
Deputy Governor
Corporate Services Sector
Bangko Sentral ng Pilipinas
Subject Matter Experts:
MS. MARICRIS A. SALUD, CPA, CISA, CISM, MSCF
Deputy Director and Head
Technology Risk and Innovation Supervision Department
Bangko Sentral ng Pilipinas
MR. DEXTER S. MACATANGAY, CPA, MBA, CISA, CIA, CISM, CC, CISSP
Manager
Cybersecurity Supervision and Oversight Group
Technology Risk and Innovation Supervision Department
Bangko Sentral ng Pilipinas
Schedule:
20 November 2026, Friday, 2:00 PM to 4:30 PM
Virtual Venue: Zoom Platform
Training Fee per Participant:
Member Institution – Php 2,800.00
Non-Member Institution – Php 3,920.00
*VAT Inclusive